From the April 2026 cumulative update, Windows enforces a new kernel driver policy that removes trust for drivers signed under the legacy cross-signed root program. Each device starts in evaluation mode. Drivers that would fail the policy are still allowed to load, but every load is logged. Once a device reaches the required uptime and reboots without logging a violation, it switches to enforcement and starts blocking those drivers.
If your devices are onboarded to Microsoft Defender for Endpoint, those audit and block events can be queried across the estate:
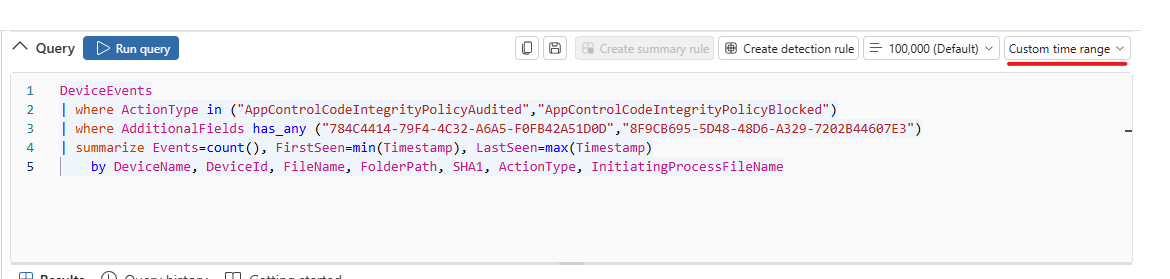
Go to Advanced Hunting (Defender portal>Expand Investigation and Response> Hunting>Advanced hunting) create a new query and paste the below.
DeviceEvents
| where ActionType in ("AppControlCodeIntegrityPolicyAudited","AppControlCodeIntegrityPolicyBlocked")
| where AdditionalFields has_any ("784C4414-79F4-4C32-A6A5-F0FB42A51D0D","8F9CB695-5D48-48D6-A329-7202B44607E3")
| summarize Events=count(), FirstSeen=min(Timestamp), LastSeen=max(Timestamp)
    by DeviceName, DeviceId, FileName, FolderPath, SHA1, ActionType, InitiatingProcessFileName
| join kind=leftouter (
    DeviceFileCertificateInfo
    | summarize arg_max(Timestamp, Signer, Issuer, IsTrusted) by SHA1
  ) on SHA1
| project DeviceName, FileName, FolderPath, ActionType, InitiatingProcessFileName, Signer, Issuer, Events, FirstSeen, LastSeen, DeviceId
| order by LastSeen desc
Top tip - don't forget to change the time frame;-
What it does
- ActionType selects App Control code integrity events. Audited means a driver would have been blocked but was allowed because the device is still in evaluation mode. Blocked means the device is enforcing and the driver was refused.
- AdditionalFields narrows the results to the Windows Driver Policy itself. The first GUID is the evaluation (audit) policy and the second is the enforcement policy. Without this filter you would also pick up other App Control policies and the vulnerable driver blocklist.
- summarize returns one row per device, driver and outcome. DeviceId is kept deliberately: if it is dropped, the record can't be linked back to an asset when you inspect it.
- InitiatingProcessFileName shows which process loaded the driver, which usually identifies the application or hardware it belongs to.
- The join adds signer and issuer details from DeviceFileCertificateInfo where MDE has collected them. A blank signer means no certificate data was collected, not that the driver is unsigned.
Reading the results
- An Audited row is a driver that will stop working once that device enforces. Each one needs a WHCP-signed replacement from the vendor.
- A Blocked row means the driver is already being refused, and something on that device is probably already broken.
- A low event count with a long gap since LastSeen points to hardware that is used only occasionally. That is the highest-risk case: each load resets the device's evaluation counter, but if the hardware goes unused for long enough the device will enforce, and the driver will be blocked the next time someone needs it.
Caveats
- An empty result does not prove a device is clean. A driver is only evaluated when it actually loads, so hardware that wasn't connected or used during the query window won't appear.
- Use the time range picker above the query editor to set the window. Advanced Hunting holds 30 days of data natively, or longer if a Microsoft Sentinel workspace is connected.
- Devices must be onboarded to MDE and running the April 2026 update or later. Otherwise the policy isn't present and no events are generated.
- To confirm on a single device, check event IDs 3076 (audited) and 3077 (blocked) in the local Microsoft-Windows-CodeIntegrity/Operational log after exercising the hardware.